Comp AI Secures $34 Million Series A to Automate Cybersecurity and Compliance in the Agentic AI Era

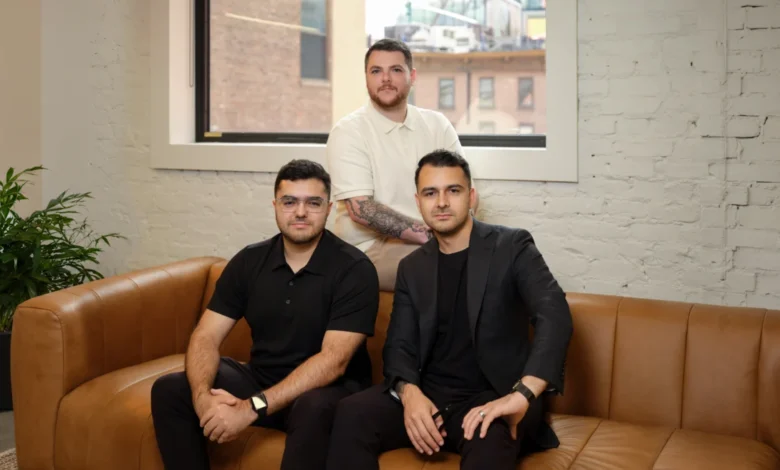
The modern enterprise landscape is undergoing a profound paradigm shift driven by the rapid adoption of artificial intelligence. As businesses increasingly deploy autonomous AI agents to manage internal operations, write code, and handle sensitive customer data, traditional frameworks for security and compliance are struggling to keep pace. Enter Comp AI, a specialized cybersecurity and compliance startup that announced Thursday the successful closure of a $34 million Series A funding round. Co-led by Roo Capital and Grand Ventures, this latest infusion of capital brings the company’s total funding to $37.5 million, underscoring the surging investor demand for automated, real-time security solutions tailored to the agentic era.
The Genesis of Comp AI: From LeapAI to Compliance Automation
Comp AI was founded in January of last year by a trio of seasoned technologists: Lewis Carhart, who serves as Chief Executive Officer; Claudio Fuentes, who acts as Chief Operating Officer; and his brother, Mariano Fuentes, who oversees technology as Chief Technology Officer.
The founding story of Comp AI is rooted in the hard-earned lessons of entrepreneurial trial and error. Before launching Comp AI, Claudio Fuentes and Mariano Fuentes had spent nearly a decade building various startups together. A few years prior to their latest venture, they crossed paths with Carhart and invited him to join them in building LeapAI, a workflow automation platform. Within this previous enterprise, Claudio Fuentes assumed the role of CEO and co-founder, Carhart spearheaded growth initiatives, and Mariano Fuentes functioned as a senior full-stack engineer.
For approximately two years, LeapAI operated and scaled impressively, eventually amassing a user base exceeding one million individuals. However, the founding team ultimately confronted a harsh business reality: despite the robust user adoption, the platform failed to establish a use case "sticky enough" to justify continued venture capital investment and long-term scaling efforts. Rather than pushing forward with a flagging product, the founders made the pragmatic decision to shut LeapAI down.
Yet, the failure of LeapAI was far from a total loss; it served as an invaluable incubation period for the team. Through building LeapAI, the founders acquired deep technical proficiency in working with Large Language Models (LLMs) and learned the critical importance of zeroing in on high-value, highly specific market use cases. Furthermore, the grueling operational experience of scaling LeapAI exposed them to one of the most notoriously painful bottlenecks in the B2B software ecosystem: the SOC 2 compliance process.
The Pain Point: Navigating Obscure Compliance Frameworks
As LeapAI grew and attempted to close deals with larger enterprise clients, the startup hit a brick wall commonly faced by early-stage tech companies: the rigorous, time-consuming demands of enterprise security compliance. For software-as-a-service (SaaS) companies, achieving and maintaining compliance certifications such as SOC 2 is not merely a bureaucratic hurdle; it is directly tied to revenue generation. Enterprise buyers routinely mandate comprehensive security audits before they are willing to sign contracts or migrate sensitive data onto a new platform.
For Claudio Fuentes, Carhart, and Mariano Fuentes, navigating this maze by hand proved to be an exhausting distraction from their core product development. Describing the experience, Claudio Fuentes noted that the process was remarkably obscure, requiring months of manual labor that continuously pulled the engineering and leadership teams away from building their actual software.
Recognizing a massive, unaddressed market inefficiency, the trio conceptualized a new enterprise. Given that the core concept originated with Carhart, the team decided that he would step into the role of CEO for this new venture, while the Fuentes brothers would leverage their deep operational and technical backgrounds as COO and CTO. Thus, Comp AI was born to eradicate the manual friction of security and compliance through automation.
Tackling the Workflow: How Comp AI’s Agentic Platform Operates
Comp AI positions itself at the vanguard of a new generation of cybersecurity companies designed specifically to help modern enterprises operate efficiently within what industry insiders call the "agentic era." The platform utilizes autonomous AI agents to shoulder the administrative burdens of security and compliance work.
Rather than forcing human workers to draft hundreds of pages of security policies from scratch or spend weeks manually collecting evidence for upcoming audits, Comp AI’s platform automates these repetitive tasks. The AI agents can draft comprehensive company security policies, gather necessary documentation and audit evidence, and perform continuous monitoring to ensure that the enterprise remains in strict adherence to its established compliance controls.
Additionally, the startup offers AI-powered penetration testing. In this capacity, the platform proactively scans codebases and underlying infrastructure to identify, isolate, and remediate vulnerabilities before malicious actors can exploit them.
Despite the heavy utilization of artificialintelligence, the founders emphasize that Comp AI is designed to augment human labor rather than replace it entirely. Independent audit reviews, human oversight, and strategic decision-making remain strictly in the hands of qualified personnel. Carhart illustrated this collaborative dynamic by explaining that while an AI agent might draft a preliminary security policy, a human worker must still review, edit, and formally approve it before implementation.
Furthermore, human oversight plays an essential role in onboarding the AI, supporting internal controls, and maintaining the stability of the agentic workflow. As artificial intelligence models grow more advanced and are granted permission to execute increasingly consequential actions, the executive team insists that the level of safeguards and mandatory human approvals must scale upward in tandem.
The Broader Market Context: The Agentic Era and Continuous Security
The funding round led by Roo Capital and Grand Ventures arrives at a time of intense industry-wide anxiety regarding the novel security risks introduced by generative artificial intelligence and autonomous agents. A crowded field of security and compliance startups—including established unicorns like Vanta and Drata—has emerged in recent years to help businesses streamline compliance. However, Comp AI’s leadership argues that legacy platforms were built for a static SaaS world, not for an environment where software mutates and deploys autonomously in real time.
Carhart points out that the rapid pace of corporate experimentation with AI has created an urgent, structural demand for continuous, highly autonomous security and compliance platforms. Traditional compliance operates on a snapshot model: a company undergoes an exhaustive audit, receives a SOC 2 certification, and assumes its security posture is locked in.
However, this traditional model fails to account for the dynamic nature of modern software development. Carhart offered a hypothetical scenario: a company successfully completes its annual SOC 2 audit, only to deploy a new AI agent two weeks later that gains access to sensitive customer data, modifies internal system permissions, or inadvertently introduces a vulnerability through automated code deployment. In such a scenario, the previous audit has not technically become invalid, but it is fundamentally incapable of communicating what has changed in the system in real time.
Echoing this sentiment, Mariano Fuentes emphasized that as modern organizations embrace increasingly complex AI architectures, they face mounting regulatory and operational pressure to maintain absolute accountability. Businesses must be able to transparently demonstrate precisely what data an AI agent accessed, what actions it attempted to execute, and whether those actions remained securely within the predefined operational boundaries established by the enterprise.
To address this challenge, Comp AI is building its foundation around granular permissions and accountability. Mariano Fuentes noted that the company is actively developing a security layer capable of monitoring, evaluating, and validating these nuanced risks on a continuous basis as enterprise AI systems continue to evolve.
Future Outlook and Product Expansion
With $34 million in fresh Series A capital now secured, Comp AI plans to aggressively scale its operations. The primary objectives for the new funding include accelerating product development, expanding engineering and go-to-market teams, and broadening the platform’s core capabilities to address an even wider array of enterprise security requirements.
As enterprises continue to race toward full-scale AI integration, the attack surface for cyber threats is expanding exponentially. By bridging the gap between rapid technological innovation and rigorous regulatory compliance, Comp AI aims to ensure that businesses do not have to sacrifice security for speed. With strong financial backing from institutional investors and a battle-tested founding team that understands the pain points of scaling tech infrastructure firsthand, Comp AI is well-positioned to become a foundational pillar of the agentic security ecosystem.